SOC 2 and audits
Your first SOC 2, step by step
Most businesses come to Vanta because a customer asked for a SOC 2 report. Here is how the path works, what the auditor looks at, and how a Trust Center keeps the next questionnaire from landing on your desk.
SOC 2 in Vanta
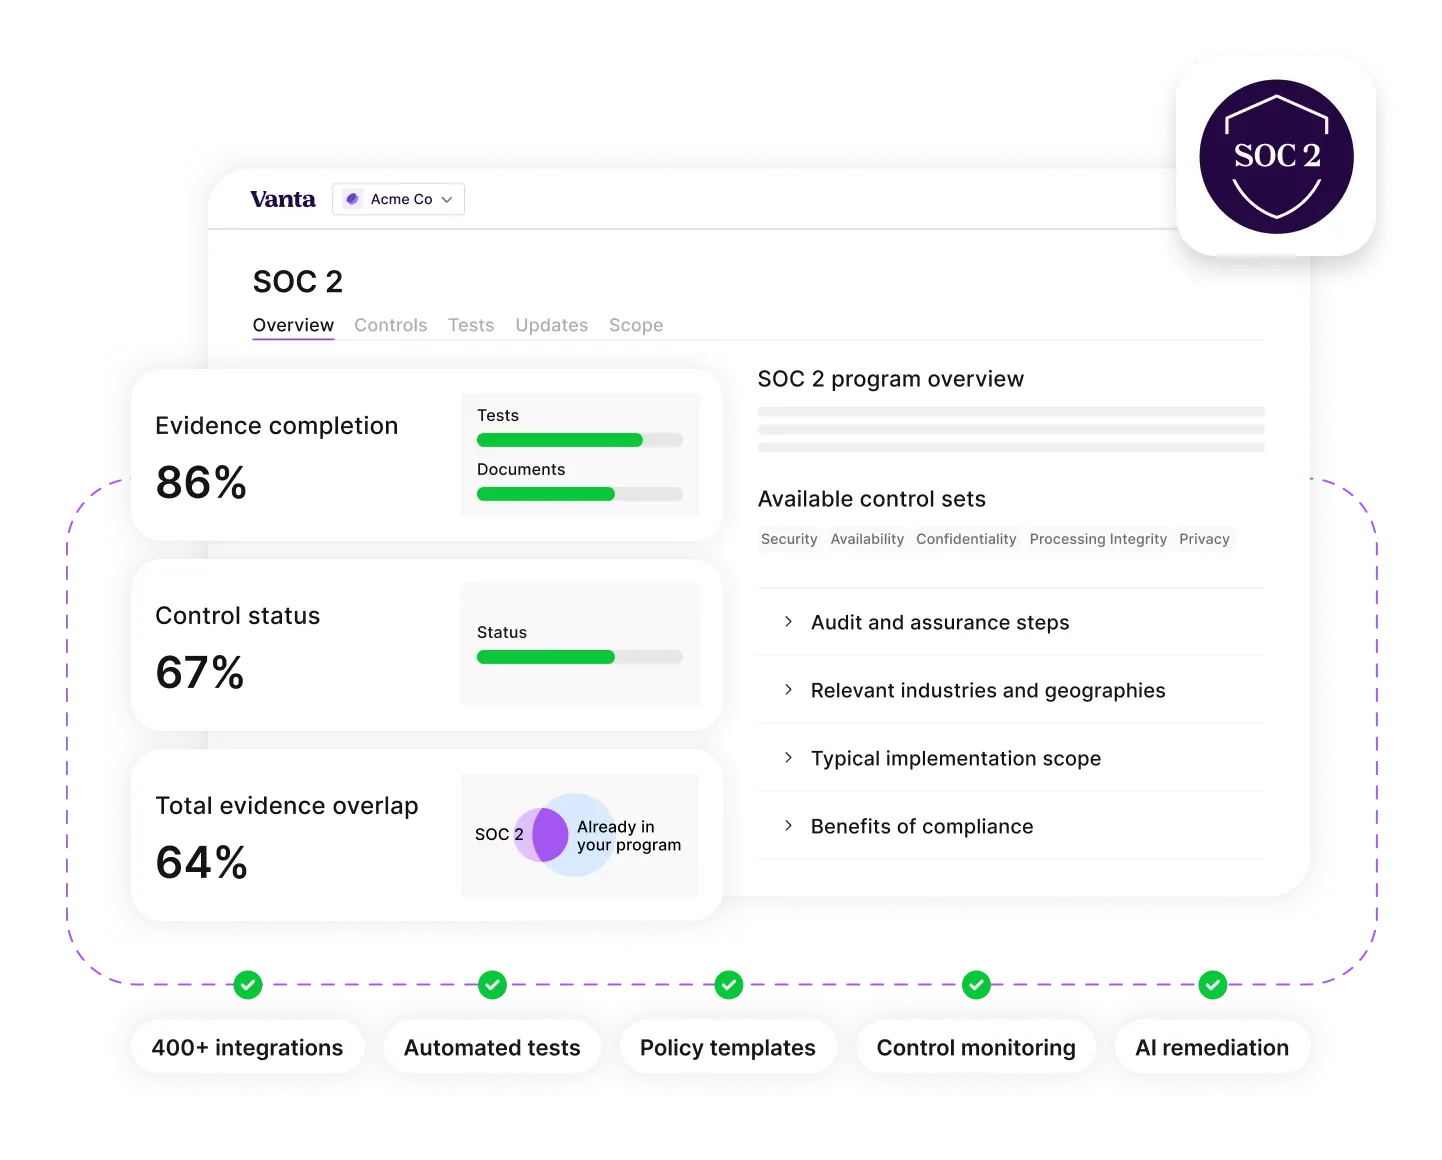
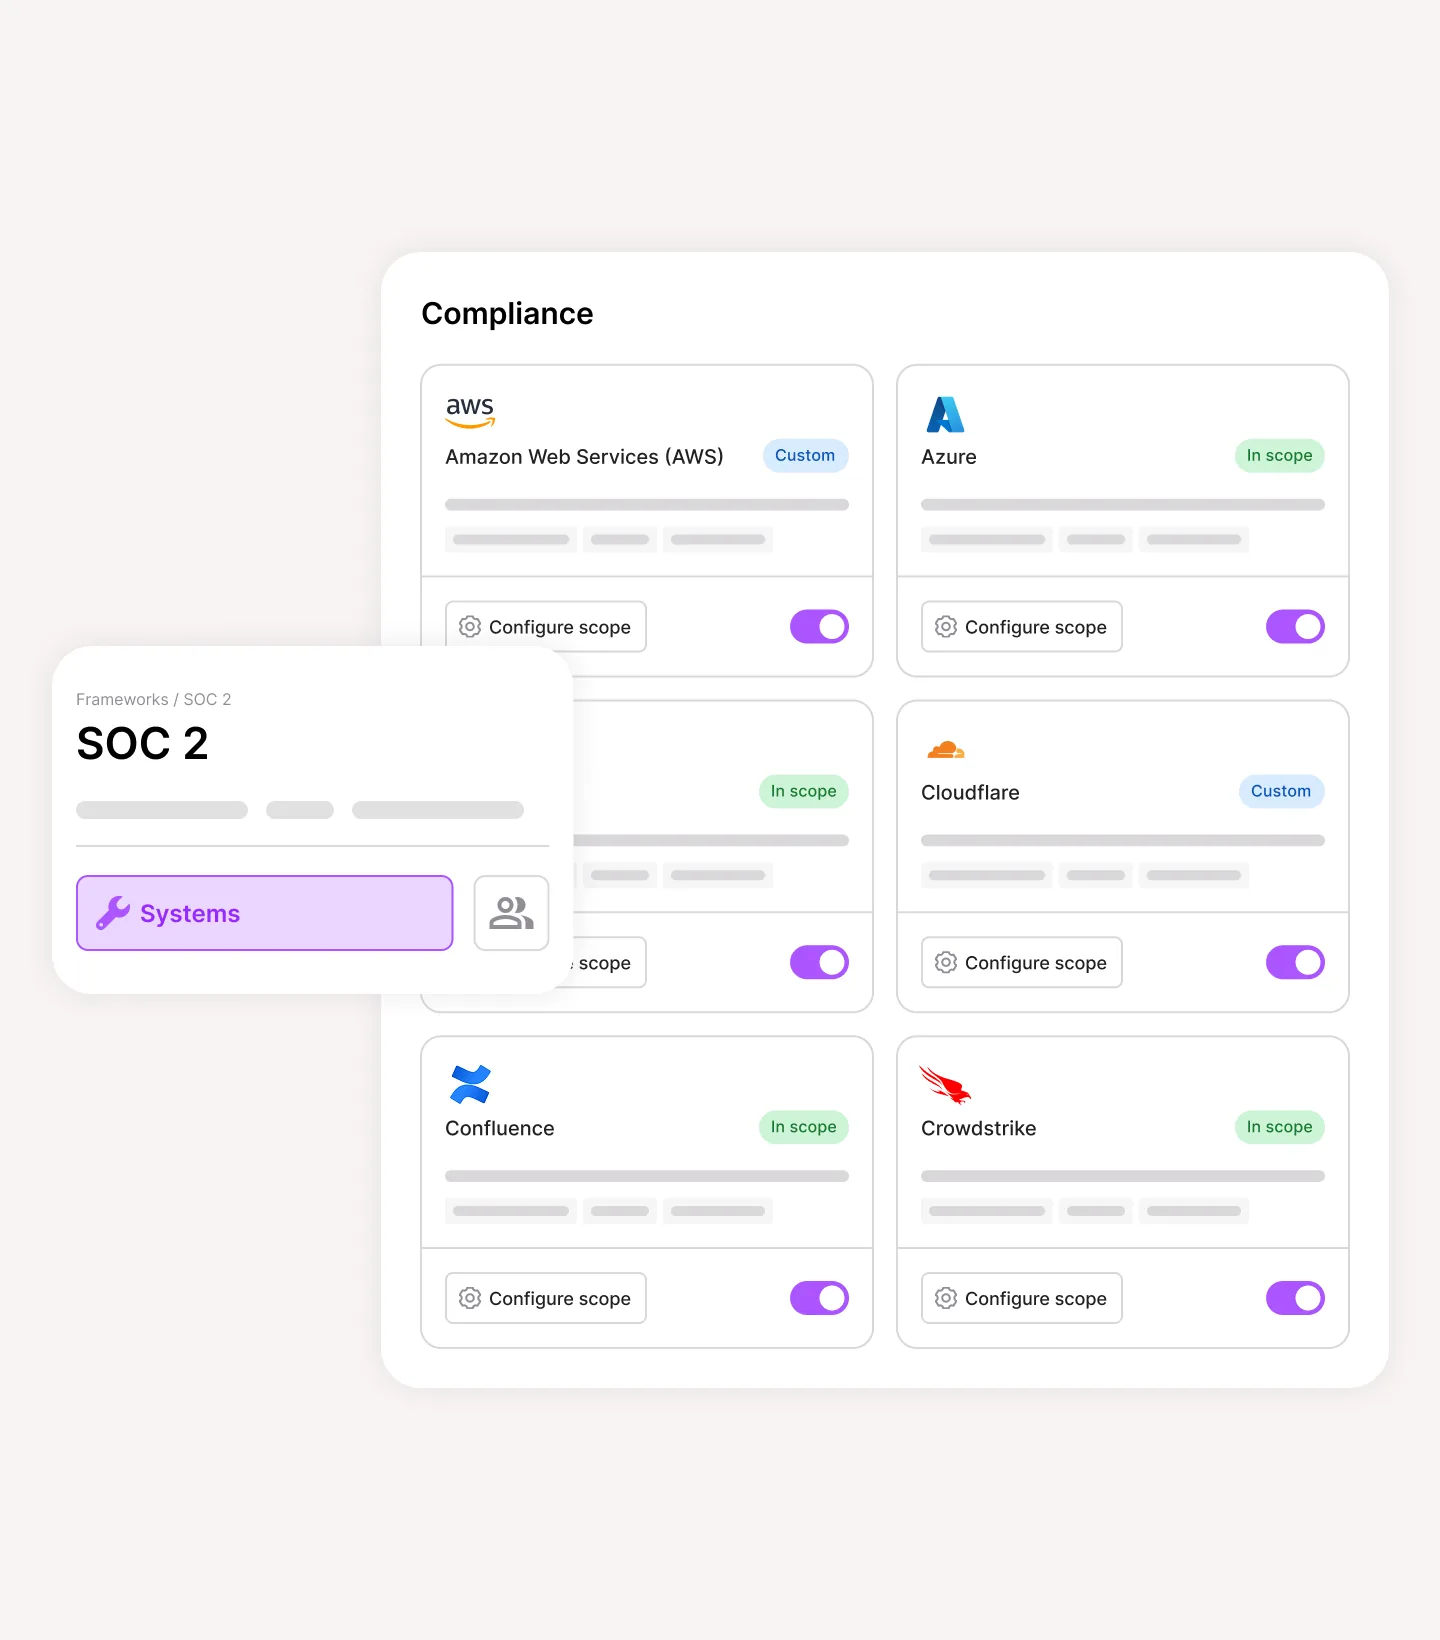
Product images: Vanta.
Type I or Type II
Two kinds of SOC 2 report
Type I
Checks that the right controls are in place as of a specific date. Vanta suggests it when speed matters.
Type II
Checks that those controls worked over a period of time. Vanta suggests it when customers want ongoing assurance.
The path
What happens, in order
- Scope itDecide which product, team or region the report covers.
- Connect systemsLink cloud, identity, code and device tools so Vanta can test them.
- Fix failing testsWork the list. Elevate handles the IT fixes such as encryption, sign-in and backups.
- Pick an auditorVanta introduces independent auditors from a network it says has 100+ firms.
- Get auditedThe auditor reviews evidence inside Vanta and issues the report.
Vanta says timing depends on your scope and pace. We give you a realistic date after the first gap review.
What the auditor looks at
The controls behind a clean report
Access control
Who can reach what, how sign-in is protected, and proof that access is reviewed and removed on time.
Change management
How code and system changes are approved, tested and recorded.
Monitoring
Logging, alerting and evidence that someone responds.
Device security
Encryption, screen lock, updates and endpoint protection on every laptop.
Policies and training
Written policies employees have accepted, plus completed security training.
Vendors
A vendor list with risk reviews for the ones that touch your data.
Trust Center
Answer security reviews before they are asked
A branded page where buyers see your security documents, live controls and AI answers without emailing your team.
Public page
Security documents, live controls and AI-powered answers for buyers.
Gated documents
Integrations with Salesforce, HubSpot, DocuSign and Ironclad automate access approvals and NDA collection.
AI answers
Visitors ask questions and Vanta AI answers from your Trust Center content.
Live controls
Real-time evidence of active controls, synced from your compliance program.
Analytics
Track downloads, page views and chatbot questions.
Your brand
Custom tags, filters, subscriber notifications and branding.
Vendor risk
Know which vendors put you at risk
Vanta finds the vendors your team uses, runs their security reviews and keeps watching them after approval.
- DiscoverFind newly adopted vendors, including shadow IT and AI tools.
- ReviewAn AI agent runs the assessment, with evidence requests and follow-ups.
- ExtractPulls findings, SLAs and security terms from SOC 2 reports, DPAs and questionnaires.
- ScoreInherent risk scoring with rubrics you can adjust.
- MonitorScans for breaches and material changes, then drafts remediation plans.
Sources: Vanta SOC 2 · Vanta Trust Center · Vanta vendor risk
A customer waiting on your SOC 2?
We will scope it with you this week and give you a real date.